mirror of
https://github.com/MobSF/Mobile-Security-Framework-MobSF.git
synced 2026-10-11 22:50:09 +00:00
HOTFIX: Android min SDK check on janus vulnerability detection (#2159)
* Android min SDK  check on janus check

* Update README.md
This commit is contained in:
 Ajin Abraham
@@ -37,6 +37,14 @@ If you liked MobSF and find it useful, please consider donating.
|
||||
*It's easy to build open source, try maintaining a project once. Long live open source!*
|
||||
|
||||
## Documentation
|
||||
|
||||
Quick setup
|
||||
|
||||
```
|
||||
docker pull opensecurity/mobile-security-framework-mobsf:latest
|
||||
docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest
|
||||
```
|
||||
|
||||
[](https://mobsf.github.io/docs)
|
||||
[](https://mobsf.github.io/docs/#/zh-cn/)
|
||||
[](https://mobsf.github.io/docs/#/ja-jp/)
|
||||
@@ -69,15 +77,6 @@ If you liked MobSF and find it useful, please consider donating.
|
||||
* For Project updates and announcements, follow [@ajinabraham](https://twitter.com/ajinabraham) or [@OpenSecurity_IN](https://twitter.com/OpenSecurity_IN).
|
||||
* Github Issues are only for tracking bugs and feature requests. Do not post support or help queries there. We have a slack channel for that.
|
||||
|
||||
### Launching MobSF Rewards
|
||||
|
||||
Contributed to MobSF? Here is a big thank you from our community to you. Claim your badge, a soulbound NFT and showcase them with pride. Let us inspire more folks !
|
||||
|
||||

|
||||
|
||||
[Claim Now!](https://aviyel.com/projects/7/mobile-security-framework/rewards)
|
||||
|
||||
|
||||
### Static Analysis - Android
|
||||
|
||||
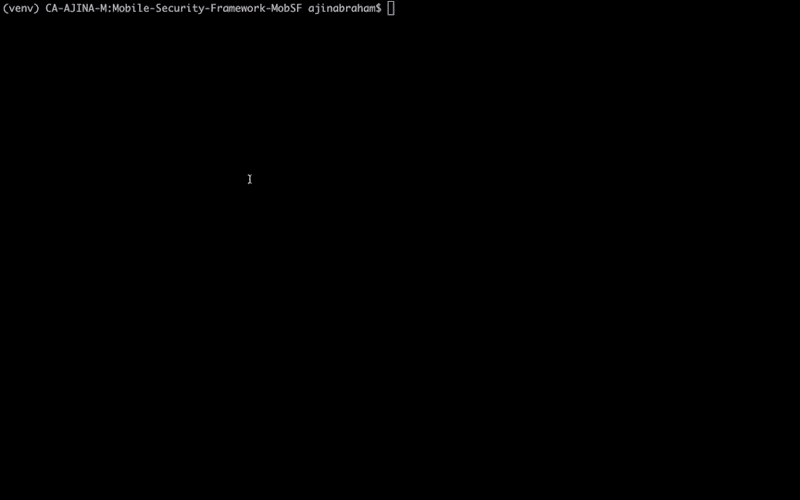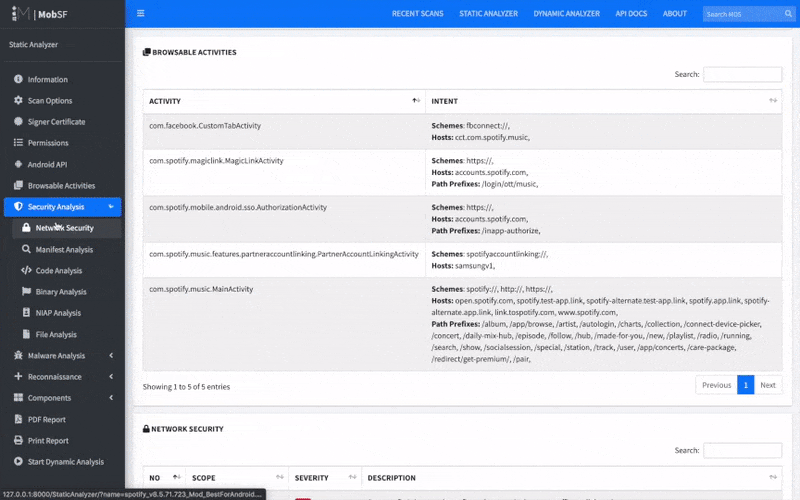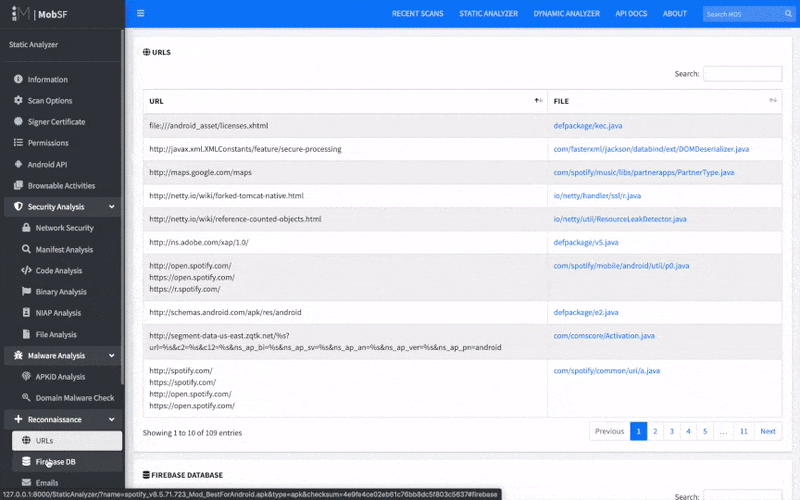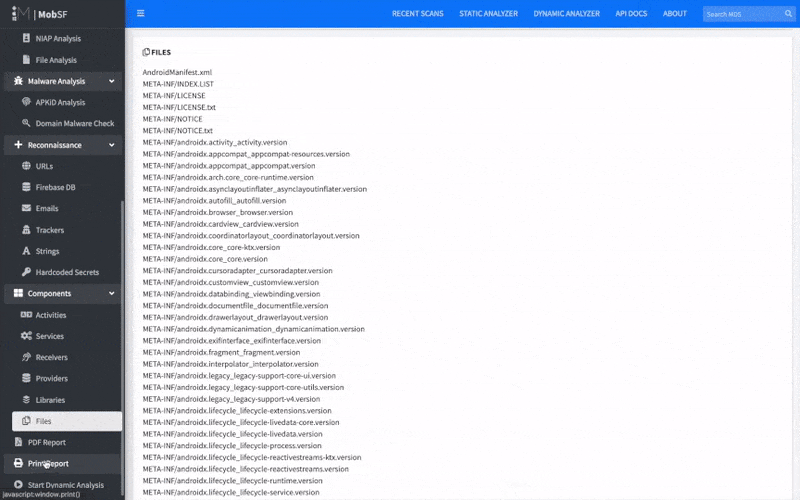
|
||||
|
||||
@@ -18,6 +18,7 @@ from django.utils.html import escape
|
||||
|
||||
logger = logging.getLogger(__name__)
|
||||
logging.getLogger('androguard').setLevel(logging.ERROR)
|
||||
ANDROID_8_1_LEVEL = 27
|
||||
|
||||
|
||||
def get_hardcoded_cert_keystore(files):
|
||||
@@ -46,7 +47,7 @@ def get_hardcoded_cert_keystore(files):
|
||||
logger.exception('Getting Hardcoded Certificates/Keystores')
|
||||
|
||||
|
||||
def cert_info(app_dir, app_file):
|
||||
def cert_info(app_dir, app_file, man_dict):
|
||||
"""Return certificate information."""
|
||||
try:
|
||||
logger.info('Reading Code Signing Certificate')
|
||||
@@ -128,7 +129,9 @@ def cert_info(app_dir, app_file):
|
||||
'Missing Code Signing certificate'))
|
||||
if a.is_signed_v1():
|
||||
status = 'high'
|
||||
if a.is_signed_v2() or a.is_signed_v3():
|
||||
api_level = int(man_dict['min_sdk'])
|
||||
if ((a.is_signed_v2() or a.is_signed_v3())
|
||||
and api_level < ANDROID_8_1_LEVEL):
|
||||
status = 'warning'
|
||||
findings.append((
|
||||
status,
|
||||
|
||||
@@ -197,7 +197,8 @@ def static_analyzer(request, api=False):
|
||||
elf_dict = elf_analysis(app_dic['app_dir'])
|
||||
cert_dic = cert_info(
|
||||
app_dic['app_dir'],
|
||||
app_dic['app_file'])
|
||||
app_dic['app_file'],
|
||||
man_data_dic)
|
||||
apkid_results = apkid_analysis(app_dic[
|
||||
'app_dir'], app_dic['app_path'], app_dic['app_name'])
|
||||
tracker = Trackers.Trackers(
|
||||
|
||||
Reference in New Issue
Block a user