 f57a3c997c
* feat: expose decompiled Android XML files via the view_source REST API

AndroidManifest.xml and other resource XML files are already
decompiled to apktool_out/ during static analysis, but there was no
way to fetch them through the API - only Java/Kotlin/smali sources
were reachable via view_source, and the standalone manifest_view
page is web-only with no API route.

Add an 'xml' type to view_source that points at apktool_out/, and
register it in the API dispatcher's Android type set (it also
covers eclipse/studio/apk/java/smali there; xml needs to be added
explicitly or it falls through to the iOS handler). .xml was
already in the allowed file extension list, so no other validation
changes were needed. Path traversal protection (is_safe_path) is
unchanged and applies to the new type like every other one.

Co-authored-by: alanhasn

* fix: safely support XML across Android scan types

Co-authored-by: Ajin Abraham <[email protected]>

* fix: validate view source API parameters

Co-authored-by: Ajin Abraham <[email protected]>

* Remove ViewSourceXMLTest

Co-authored-by: Ajin Abraham <[email protected]>

* fix: address CodeQL findings on Android view_source

Use validated form cleaned_data for path construction, keep
exception details out of JSON error responses, and annotate
post-validation path checks as known CodeQL false positives.

Co-authored-by: Ajin Abraham <[email protected]>

---------

Co-authored-by: Ajin Abraham <[email protected]>
Co-authored-by: Cursor Agent <[email protected]>
Mobile Security Framework (MobSF)

Mobile Security Framework (MobSF) is a security research platform for mobile applications in Android, iOS and Windows Mobile. MobSF can be used for a variety of use cases such as mobile application security, penetration testing, malware analysis, and privacy analysis. The Static Analyzer supports popular mobile app binaries like APK, IPA, APPX and source code. Meanwhile, the Dynamic Analyzer supports both Android and iOS applications and offers a platform for interactive instrumented testing, runtime data and network traffic analysis. MobSF seamlessly integrates with your DevSecOps or CI/CD pipeline, facilitated by REST APIs and CLI tools, enhancing your security workflow with ease.
Made with  in India




MobSF is also bundled with Android Tamer, BlackArch and Pentoo.
Support MobSF

Has MobSF made a difference for you? Show your support and help us innovate with a donation. It's easy to build open source, maintaining one is a different story.
Long live open source!
Documentation
Quick setup with docker
docker pull opensecurity/mobile-security-framework-mobsf:latest
docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest

# Default username and password: mobsf/mobsf

- Try MobSF Static Analyzer Online: mobsf.live
- MobSF in CI/CD: mobsfscan
- Conference Presentations: Slides & Videos
- MobSF Online Course: OpSecX MAS
- What's New: See Changelog
Collaborators
Ajin Abraham  | Magaofei
 | Matan Dobrushin
 | Vincent Nadal

e-Learning Courses & Certifications
 Automated Mobile Application Security Assessment with MobSF -MAS
 Android Security Tools Expert -ATX
MobSF Support
- Free Support: Free limited support, questions, help and discussions, join our Slack channel
- Enterprise Support: Priority feature requests, live support & onsite training, see

Contribution, Feature Requests & Bugs
- Read CONTRIBUTING.md before opening bugs, feature requests and pull request.
- For Project updates and announcements, follow @ajinabraham or @OpenSecurity_IN.
- Github Issues are only for tracking bugs and feature requests. Do not post support or help queries there. We have a slack channel for that.
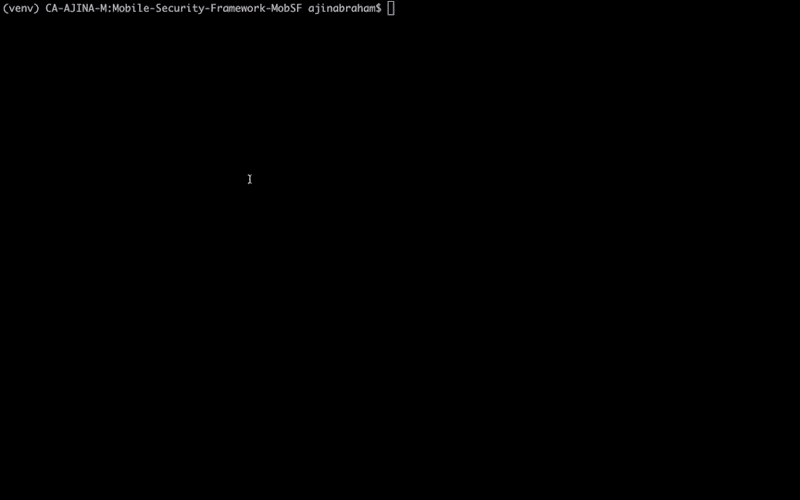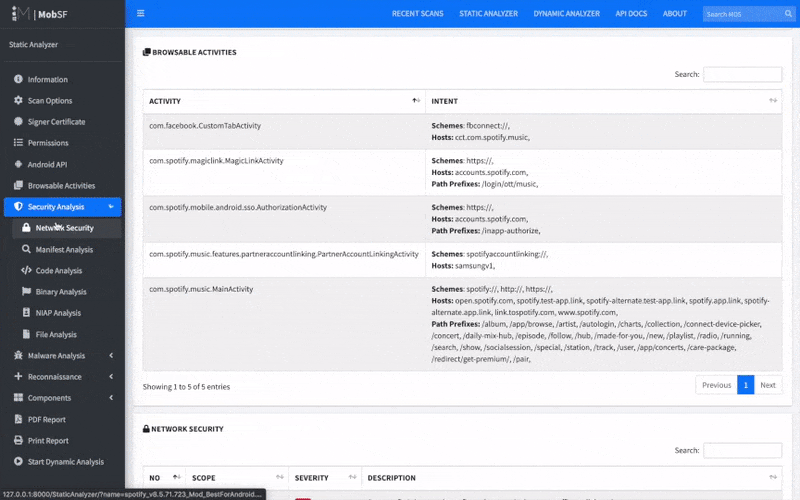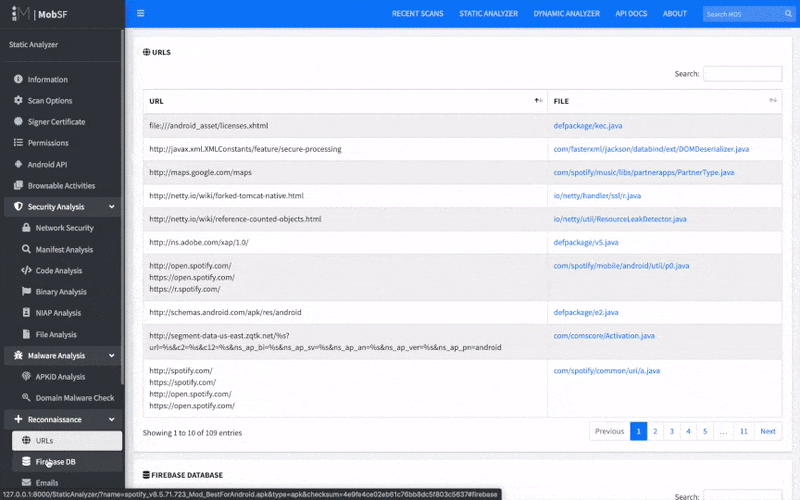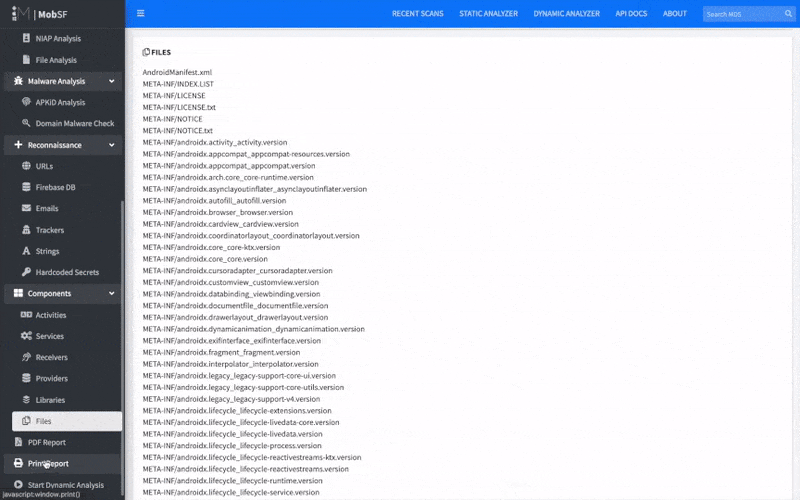
Static Analysis - Android
Static Analysis - iOS

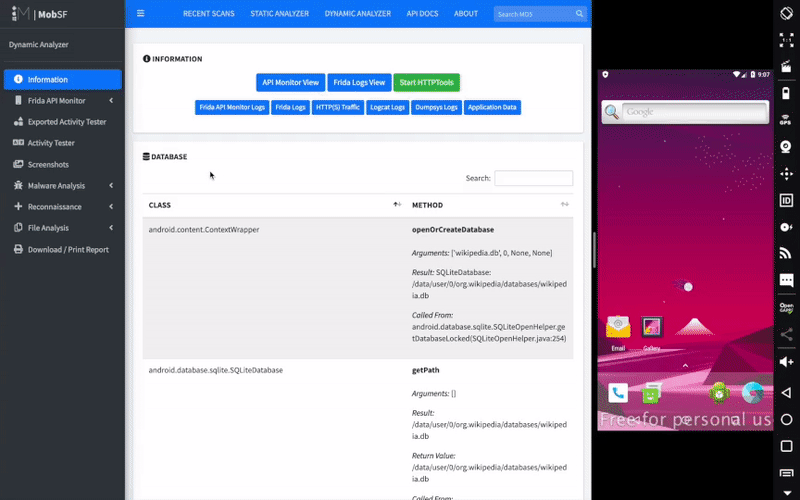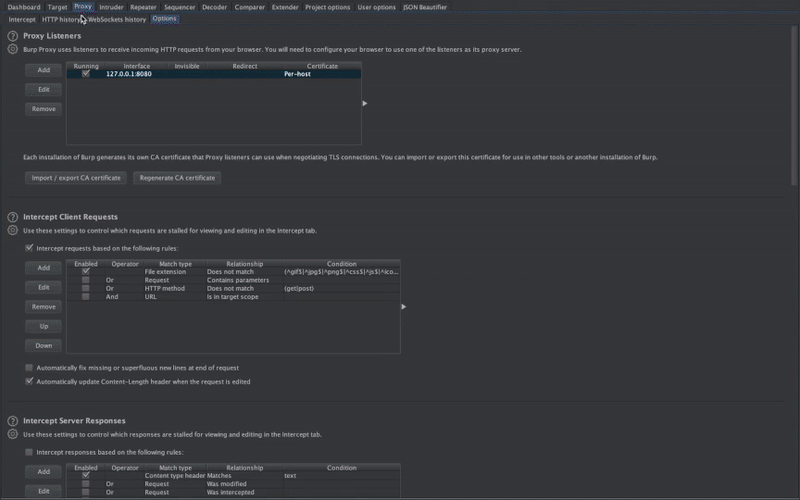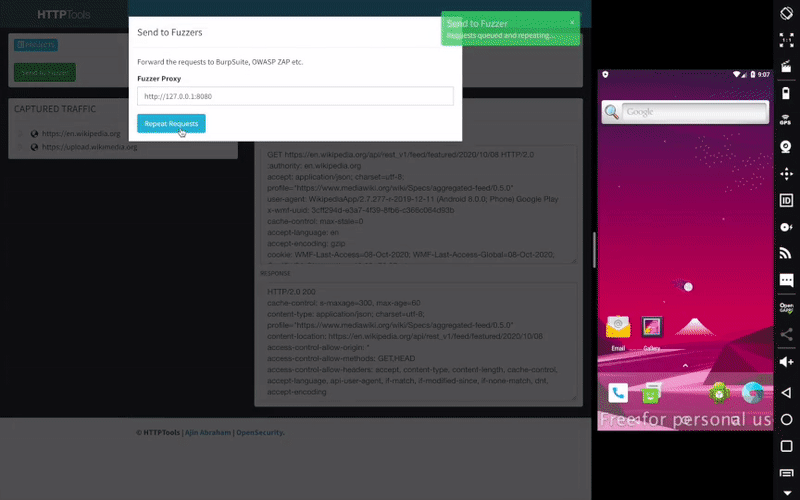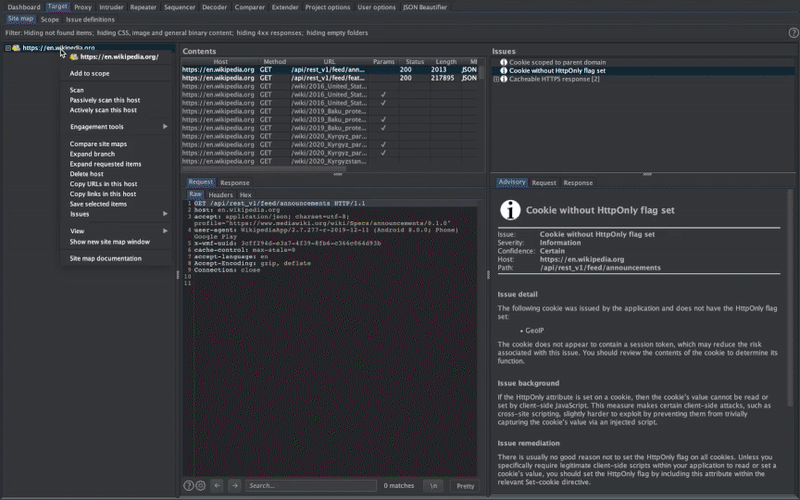
Dynamic Analysis - Android APK

Web API Viewer
Dynamic Analysis - iOS IPA
Past Collaborators

Honorable Contributors & Shoutouts
- Amrutha VC - For the new MobSF logo
- Dominik Schlecht - For the awesome work on adding Windows Phone App Static Analysis to MobSF
- Esteban - Better Android Manifest Analysis and Static Analysis Improvement.
- Matan Dobrushin - For adding Android ARM Emulator support to MobSF - Special thanks goes for cuckoo-droid
- Shuxin - Android Binary Analysis
- Abhinav Saxena - (@xandfury) - For Travis CI and Logging integration
 Netguru (@karolpiateknet, @mtbrzeski) - For iOS Swift support, Rule contributions and SAST refactoring.
- Maxime Fawe - (@Arenash13) - For Matching Strategy implementation of SAST pattern matching algorithms.
- Abhinav Sejpal (@Abhinav_Sejpal) - For poking me with bugs, feature requests, and UI & UX suggestions
- Anant Srivastava (@anantshri) - For Activity Tester Idea
- Anto Joseph (@antojoseph) - For the help with SuperSU
- Bharadwaj Machiraju (@tunnelshade) - For writing pyWebProxy from scratch
- Rahul (@c0dist) - Kali Support
- MindMac - For writing Android Blue Pill
- Oscar Alfonso Diaz - (@OscarAkaElvis) - For Dockerfile contributions
- Thomas Abraham - For JS Hacks on UI
- Tim Brown (@timb_machine) - For the iOS Binary Analysis Ruleset
- Shanil Prasad (@Rajuraju14) - For improving iOS ATS Analysis
- Jovan Petrovic (@JovanPetrovic) - For sponsoring a server to host mobsf.live